July 2027 Is Coming: How Cruise Lines Can Turn U.S. Coast Guard Cybersecurity Rules Into Operational Readiness
Best Practices for Cyber Drills and Exercises for New USGC Rules
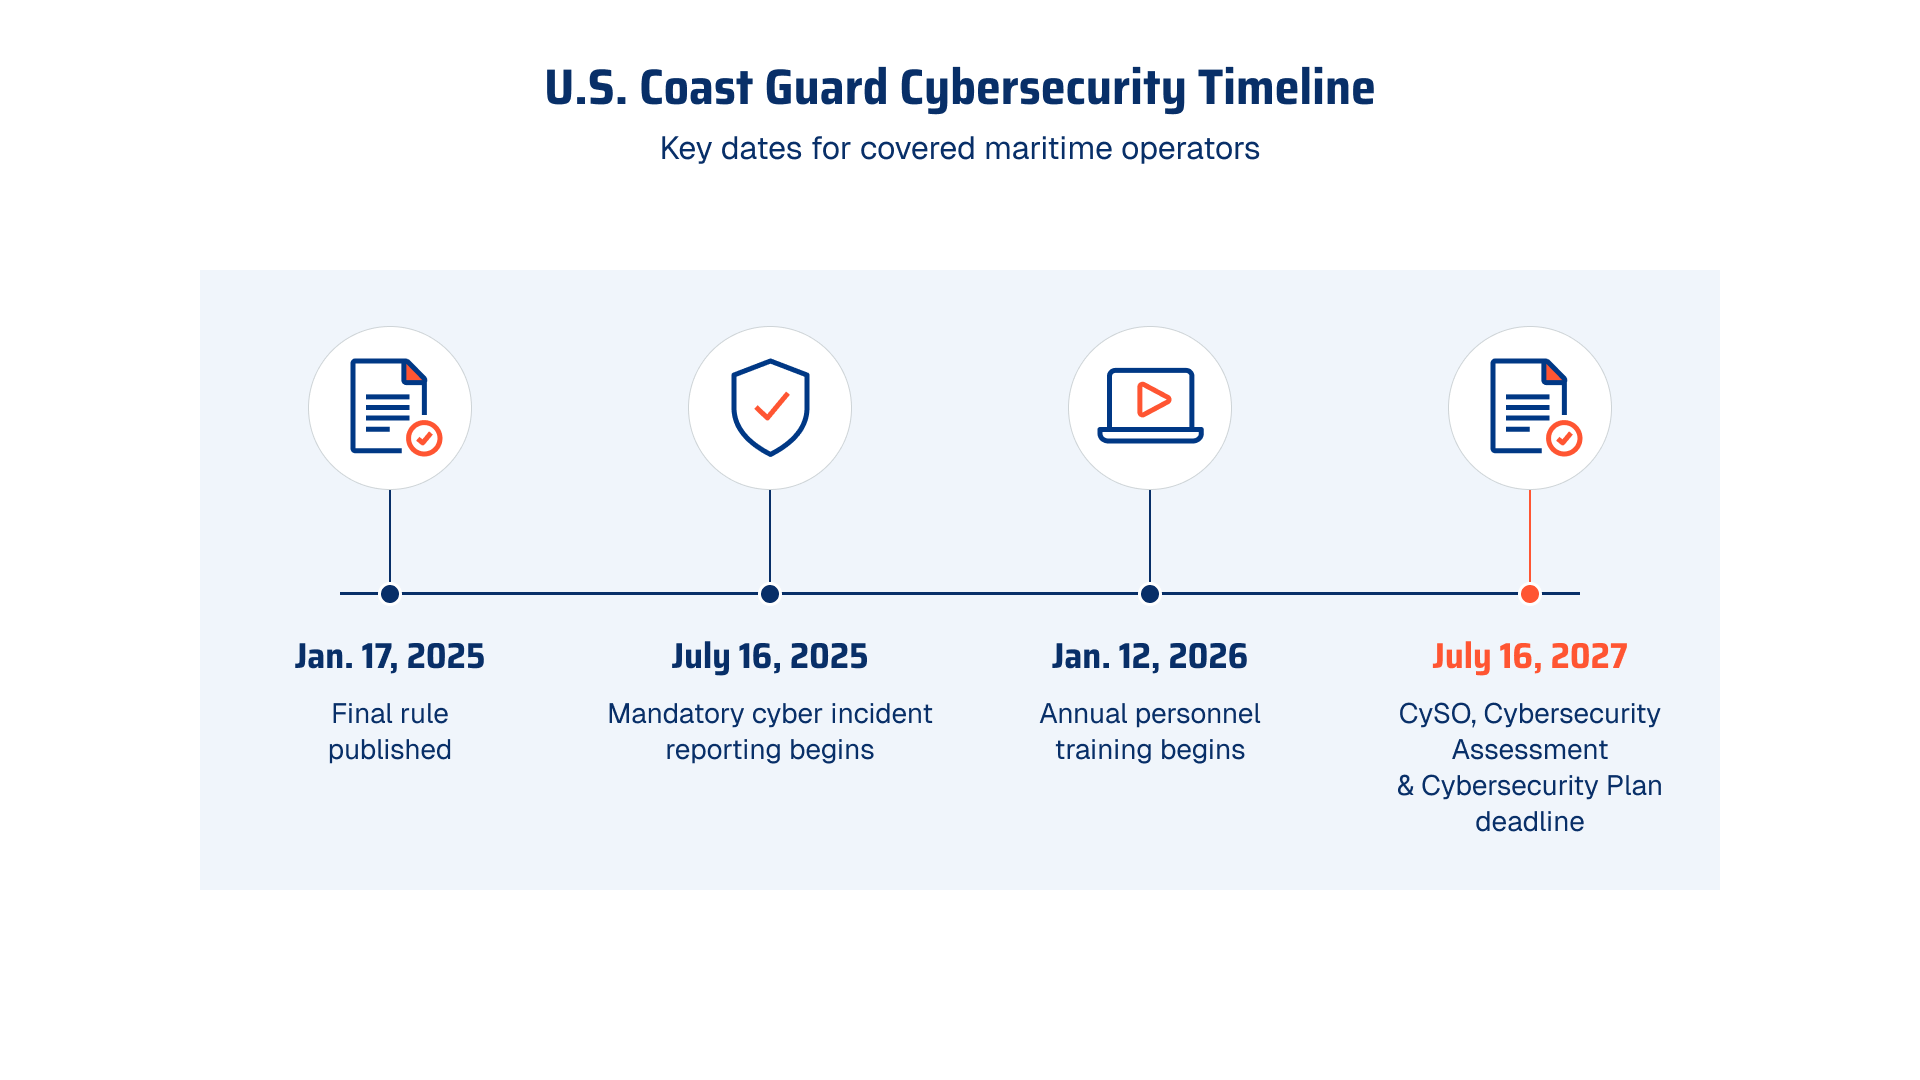
On January 17, 2025, the US Coast Guard published a series of new rules affecting the Marine Transportation System, to include vessels docking in the US, US Terminals, and OCS Facility. Effective on July 16, 2025 were requirements to report cyber security incidents to the National Response Center. Then on January 12, 2026, the training requirement became active, but most of these new rules will come into effect on July 16, 2027.
These requirements are around designating a CySO (and their responsibilities), conducting a Cyber Security Assessment, and submitting a Cyber Security plan for approval (USCG). These new requirements are daily comprehensive and have a long list of requirements for them, which can be found in their entirety in Title 33, Chapter I, Subchapter H, Part 101, Subpart F of the US Code.
The new requirements touch on various aspects of cybersecurity, but there are several that BreachRx is specifically designed to help you navigate and fulfill. These surround the following areas:
- Cyber Incident Response Plans
- Tabletop Exercises
- Drills
- Documentation
- Secure Data Retention
The BreachRx Rex Platform is a Cyber Incident Response Management (CIRM) solution that hosts and executes incident response plans during an event or exercise, and provides compliance required documentation. The platform was designed by practitioners from the ground up, from both the cybersecurity and legal fields, and is enhanced through AI features that are siloed and secured. Our company has experience helping customers across various verticals (including the transportation industry) set up response plans and navigate compliance requirements like the ones that will soon take effect from the US Coast Guard.
Cyber Incident Response Plans
In 33 C.F.R. § 101.625, the US Coast Guard specifically states that the CySO role is responsible for the creation and execution of the Cyber Incident Response plan. While creating a word document detailing what the response plan is the first step, we have found that execution of a word document during an incident tends to be inconsistent at best and that it is extremely hard to prove that they were followed properly.
The BreachRx Rex Platform provides a space where your plan can live dynamically, provide consistency, and easily deliver evidence of proper execution. We start by uploading Incident Response plans into the system (either through AI or with our world class Customer Success team). These plans get broken out into tasks that can get assigned to members of the response team and all actions are tracked and stored within the platform, allowing for easy documentation production in the case of an audit.
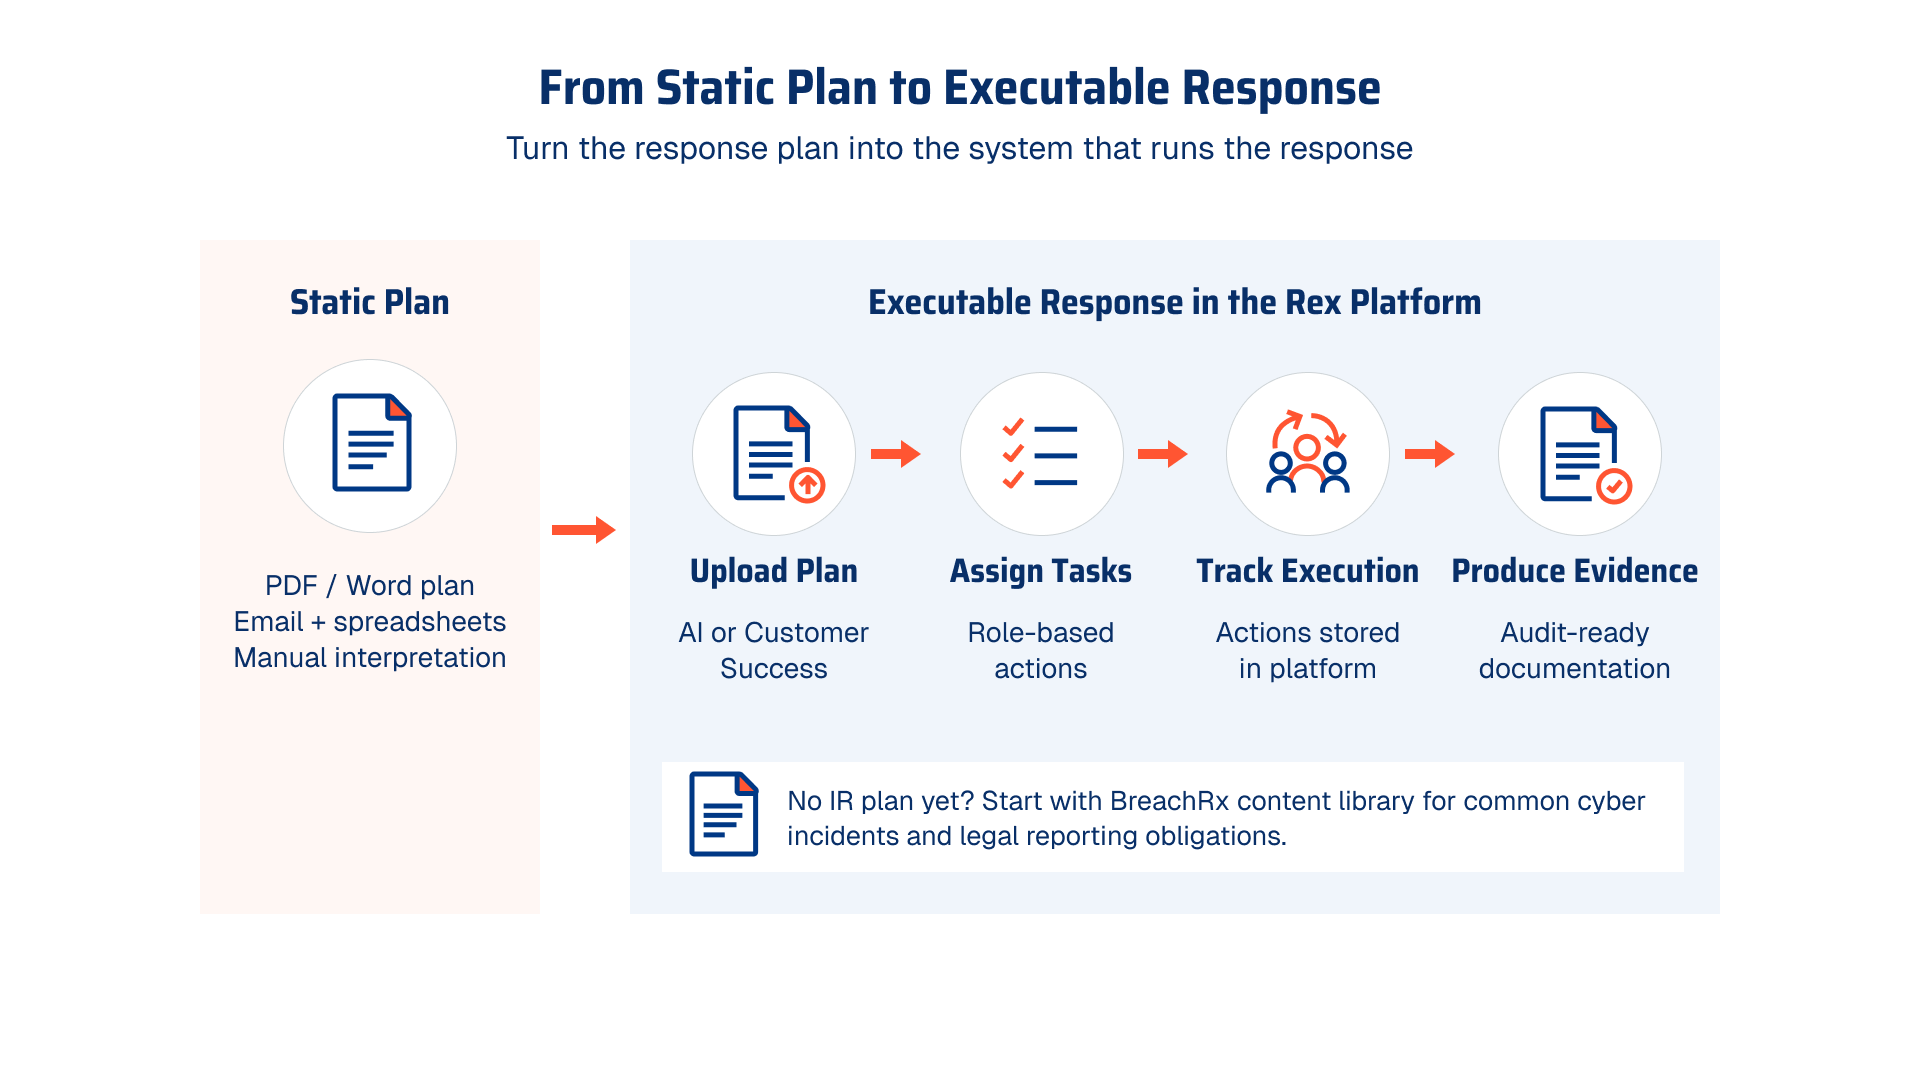
Even if you don’t have an IRP at the moment, BreachRx has a content library of response plans covering common cybersecurity incidents and legal reporting obligations that are maintained by our security and legal professionals. The platform takes the guesswork out of incident response execution and peace of mind when it comes to producing evidence, protecting your CySO.
Tabletop Exercises
33 C.F.R. § 101.635 also states that the Cybersecurity Response Plan must be used to exercise within a yearly tabletop exercise and 33 C.F.R. § 101.635 gives further details on exercise requirements.
Since The BreachRx Rex Platform can be used to host your response plans, it is the perfect place to run an exercise testing said plans. Our tabletops utilize our “Exercise” function, which allows you to run a mock incident utilizing your active response plans. It is part of our mentality of training like you fight. To further facilitate this, every BreachRx customer gets a fully facilitated tabletop exercise each year. Our services team has experience running tabletops with various fortune 500 companies and can guide you through the process.
BreachRx Tabletops are also unique in that they aren’t powerpoint driven, but response driven. As the injects appear, your team will work through it utilizing your response plans and capturing their actions and decisions. This allows for you to generate afteraction reports and lessons learned reports utilizing our hyper focused AI agents.
Of note, according to 33 C.F.R. § 101.635 (c),(4) there are requirements that “Each exercise must test communication and notification procedures and elements of coordination, resource availability, and response.” and this is a great way of showing those procedures in action.
Drills
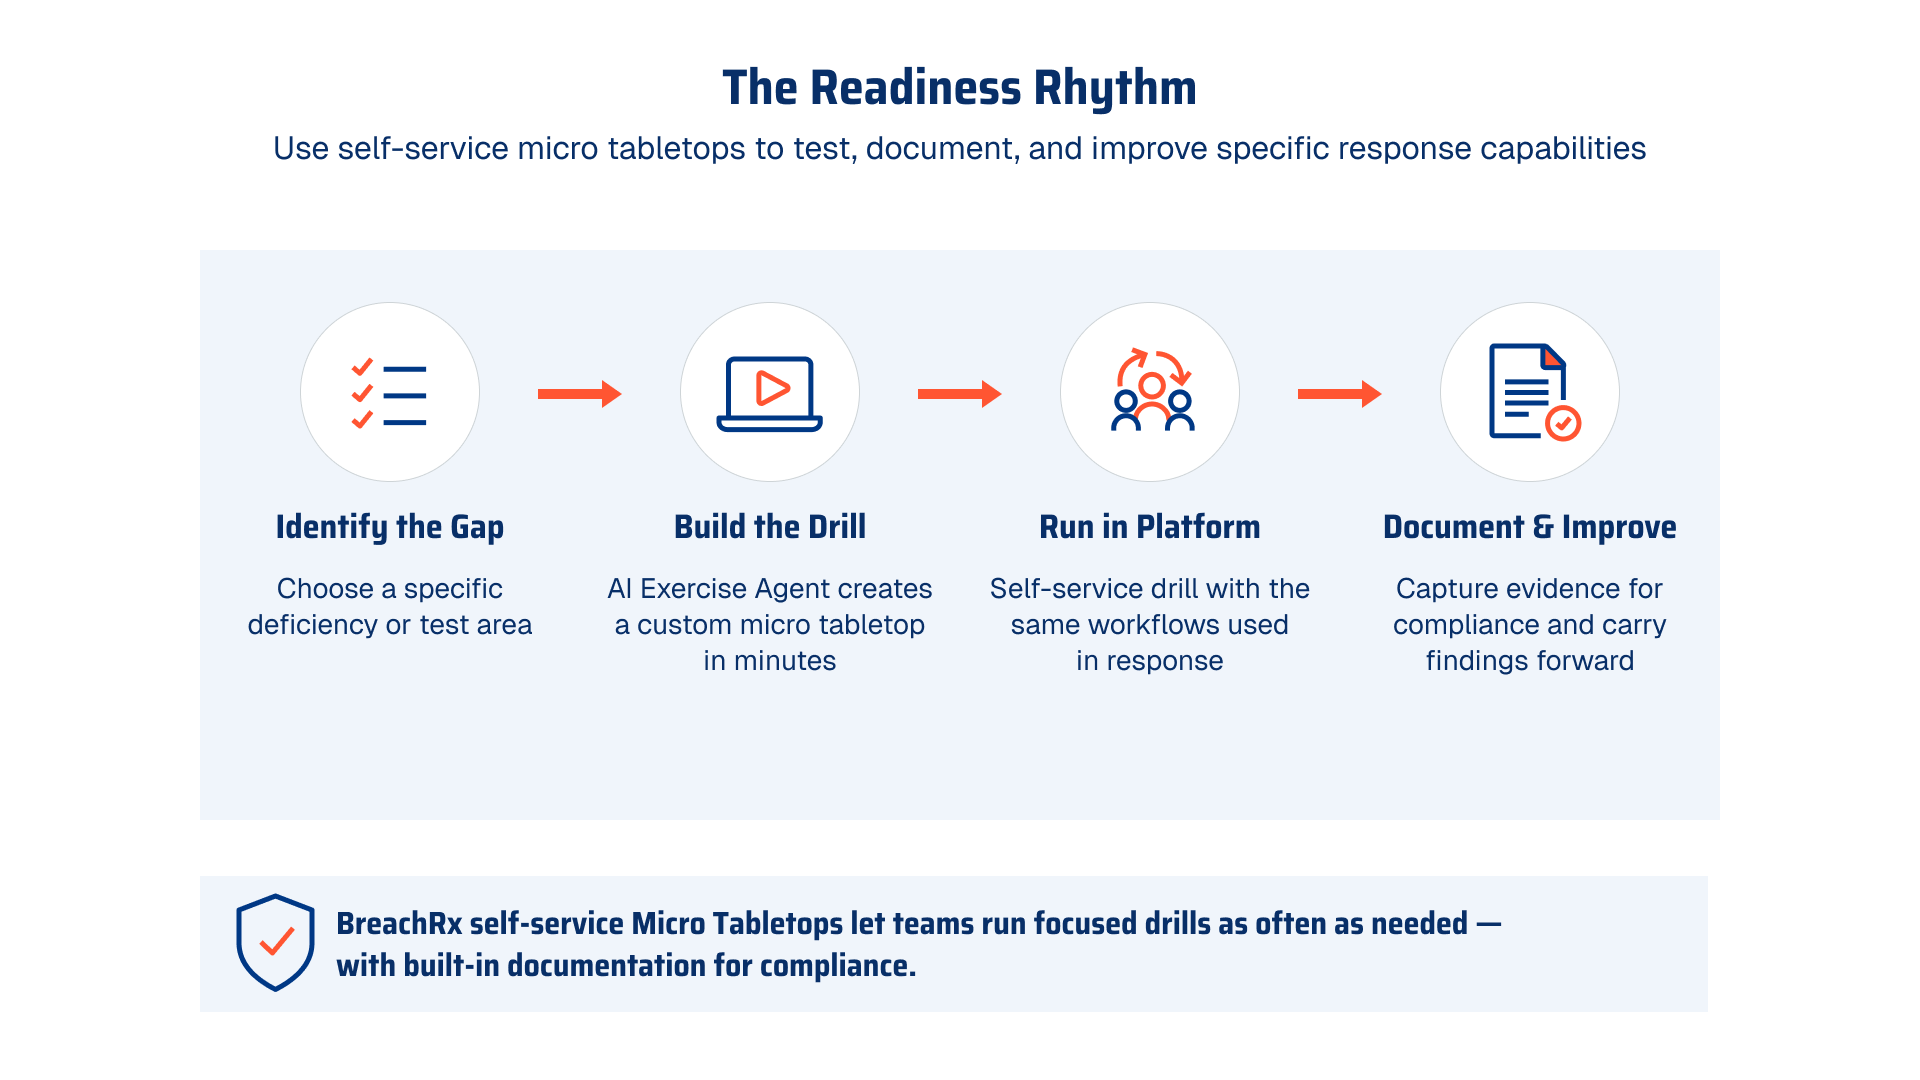
33 C.F.R. § 101.635 (b) also gives guidance for drills. Two drills must be conducted a year, these can be smaller, but should be focused on addressing a specific deficiency or test a specific area.
This is where BreachRx’s self service Micro Tabletops come into play. You can use the AI exercise agent in BreachRx to provide goals and requirements and get a custom tabletop built in platform in minutes (see our recent blog post on the topic for more information). Our team provides facilitation training and you can run as many of these in the platform as you need on your own. Drills similarly have documentation requirements, and since they use the same format as exercises in the BreachRx platform, you can generate the same level of documentation needed for compliance.
Documentation
As mentioned in the previous sections, BreachRx can provide documentation on your Exercises and Drills. Similarly, it can also provide documentation on your incident response plans themselves, as well as any incidents that you manage within the platform, satisfying the paper requirements from the Coast Guard.
Secure Storage
Finally, in 33 C.F.R. § 101.640, states that all records for Tabletop Exercises, Drills, and incidents must be kept for 2 years and made available to the Coast Guard upon request. It goes on to state that if these records are to be kept in an electronic format that “they must be protected against unauthorized access, deletion, destruction, amendment, and disclosure.”
BreachRx is an out of band incident response solution with access controls and audit logs that can protect your data and meet these secure storage requirements.
Final Thoughts
These new rules are some of the first major cyber security requirements for the maritime transportation industry and they are requiring some new motions and changes. BreachRx wants to help companies respond to incidents more effectively and assist professionals in meeting compliance requirements.
Request a demo to see how The Rex Platform can help cruise operators address Coast Guard cybersecurity requirements by operationalizing incident plans, running required drills and exercises, maintaining trusted communications, and capturing a defensible incident record.